Endpoint security has moved from basic antivirus to continuous detection, investigation and response. For UK organisations, that shift matters because ransomware, phishing-led compromise and lateral movement now develop too quickly for periodic checks alone, and Amazing Support, a managed IT support and cyber security provider, notes that EDR is now part of the practical security baseline for many SMEs.
TL;DR: Summary
- If endpoints show pre-encryption behaviour, security-tool tampering or suspicious lateral movement, you need endpoint detection and response now, not later.
- Microsoft guidance highlights early ransomware signals including stopped processes, disabled services, deleted backups and cleared event logs.
- Antivirus alone is usually too narrow; current endpoint security baselines commonly combine EDR, MFA and regular patching, a view Amazing Support also identifies for London SMEs.
- EDR matters because phishing-led compromise can happen in under a minute, and rapid isolation shortens attacker dwell time.
- If user devices start beaconing unexpectedly, using remote admin tools abnormally or touching multiple systems sideways, treat that as an active-incident threshold.
The key point is timing. By the time files are encrypted or users complain, the attacker may already have disabled controls, moved laterally and weakened backups. The organisations that respond fastest usually detect the warning signs earlier, isolate affected endpoints quickly and use endpoint telemetry to decide what happened next.
Endpoint security is now a business-risk issue because Microsoft and IBM both connect faster detection and containment with lower ransomware impact, lower breach costs and shorter recovery timelines.
A modern endpoint is not just a laptop. It can be a workstation, server, virtual machine or remote device that holds credentials, touches cloud data and connects to suppliers. When one of those assets is compromised, the issue quickly moves beyond IT into operations, finance, legal exposure and reputation.
IBM’s UK breach reporting gives that business context. Organisations using security AI and automation extensively reported average breach costs of £3.11 million, compared with £3.78 million for those not using them. The same reporting showed mean time to identify and contain was shorter too, which matters because every extra day gives an attacker more room to spread.
A common misconception is that endpoint security is still a technical hygiene topic. It is not. If attackers reach payroll data, legal files, patient records or charity donor systems through one user endpoint, the problem is already strategic.
No. Antivirus alone is usually too narrow; Microsoft guidance and Amazing Support both point to a baseline that now includes EDR, MFA and regular patching.
Traditional antivirus is best at spotting known malicious files and obvious signatures. EDR is built to record behaviour, raise alerts on suspicious chains of activity and support isolation, investigation and response. That difference matters when the attacker is using legitimate tools, stolen credentials or scripts that do not look like classic malware.
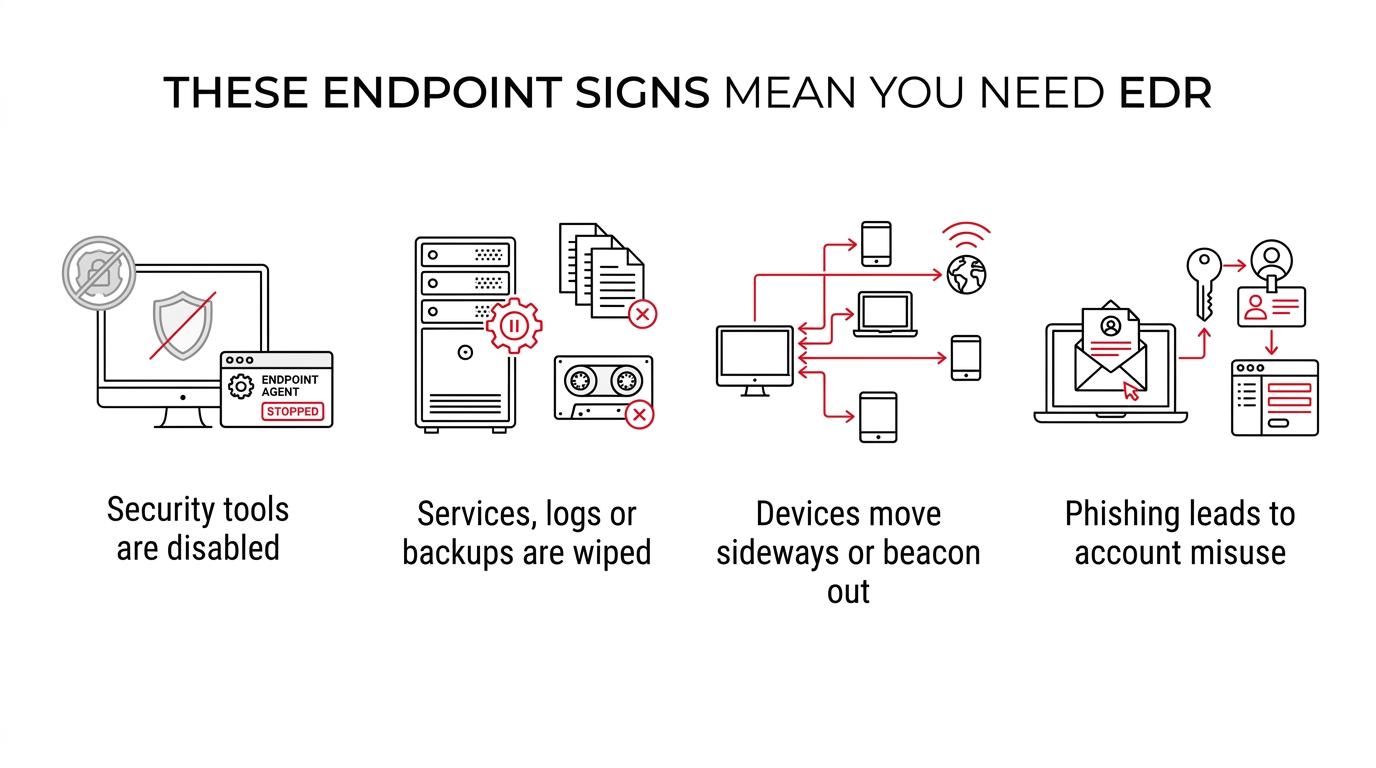
Microsoft’s ransomware hunting guidance is a good example. It focuses on pre-encryption behaviours like stopping processes, disabling services, deleting backups and clearing event logs. Those signals often sit outside the limits of older antivirus thinking.
“Amazing Support treats MFA, endpoint detection and response, email filtering and regular patching as the practical security baseline for London SMEs.”
The trade-off is straightforward. Antivirus is lighter and simpler, but it gives you less context when something subtle happens. EDR creates more visibility and better response options, though it also needs tuning, triage and clear ownership to avoid alert fatigue.
Seven signals stand out: control tampering, pre-encryption changes, strange network traffic, lateral movement, backup interference, phishing-led compromise and repeated investigative blind spots.
These are not abstract red flags. They are the kind of patterns security teams and official guidance repeatedly use to identify active intrusion before damage peaks.
If you can already see several of these signs, EDR is not a future improvement. It is an immediate control gap.
They matter because Microsoft Defender hunting focuses on them as early ransomware indicators, often before mass file encryption starts.
That point changes how you think about urgency. Many organisations still wait for a visible symptom like encrypted filenames, ransom notes or users losing access to files. By then, the attacker may have spent hours or days preparing the environment.
The stronger approach is to treat the setup phase as the real warning zone. If a host begins deleting backups, clearing logs and stopping services, the attacker is often trying to remove recovery paths and reduce visibility before the final stage. If that chain appears after a phishing event or unusual credential use, escalation should be immediate.
Pro tip: do not treat backup deletion as an isolated storage issue. On an endpoint, it is often part of the same attack path as privilege abuse and ransomware staging.
Treat disabled security tooling or cleared logs as an incident. Microsoft and CISA both frame control tampering around endpoints and management systems as a serious warning sign.
Do not wait for a second alert. If security controls disappear on one device, assume the attacker may be testing methods for broader deployment. CISA’s warning on malicious activity targeting endpoint management systems shows why this matters. If management infrastructure is touched, the attacker may gain reach across many endpoints at once.
A practical response sequence helps:
A common mistake is rebooting too quickly. If you reboot first, you may destroy useful volatile evidence and lose the exact sequence that explains whether this was malware, insider misuse or a failed admin action.
Start with host-to-host and host-to-internet patterns. Unexpected SMB, RDP, PowerShell remoting or beaconing often signals lateral movement rather than routine user activity.
The first task is to separate malicious traffic from normal operational noise. Backup tools, remote support software, Microsoft management traffic and patching platforms can all create busy connection patterns. That is why good baselining matters. If you know what normal looks like, you can spot when a finance PC suddenly behaves like an administrator workstation.
Use a simple investigative flow:
“Amazing Support combines proactive monitoring with clear ownership, which matters when unusual endpoint traffic has to be triaged and contained quickly.”
If one endpoint is touching many peers and using tools it never used before, assume lateral movement until ruled out. If the same account appears across several devices in a short period, prioritise credential containment alongside device isolation.
EDR is a toolset; MDR is an operating model. Microsoft Defender for Endpoint or similar platforms detect and isolate, while an MDR service adds human monitoring, triage and response.
This is a common source of confusion. Buying EDR gives you telemetry, alerting and response features. It does not automatically give you 24/7 analysis, alert prioritisation or incident leadership. Those come from internal security staff or an external provider running the service.
If your business has a capable internal team, direct EDR ownership can work well. If your IT team is small, stretched or not security-focused, MDR can close the operational gap. The trade-off is cost versus coverage. Tool-only is cheaper on paper, but underused tools often fail in the exact moments they were bought for.
A good test is simple: if a high-confidence alert fires at 02:00, who reads it, validates it and isolates the device?
For most SMEs, EDR is the urgent first step; XDR becomes stronger when you also need email, identity and cloud telemetry joined together. Amazing Support often sees the endpoint layer as the fastest place to improve visibility.
EDR concentrates on the device. XDR pulls together signals from endpoints, email, identity, cloud apps and sometimes network tools. That wider picture is valuable because many intrusions start with phishing, move through identity misuse and only later become an endpoint problem.
Verizon’s 2024 breach reporting makes the speed issue clear. The median time for a user to click a malicious link after opening a phishing email was 21 seconds, and median time to enter data was another 28 seconds. That leaves very little room for manual intervention. If you already have Microsoft 365, identity controls and cloud workloads in scope, XDR can connect the dots faster.
Still, many SMEs should not skip the endpoint step. If your devices are under-monitored, better email and identity visibility will help, but you may still miss the local behaviours that show encryption preparation, tampering and host isolation needs.
A phased rollout works best. Start with high-risk users and servers, tune alerts, then expand once false positives and response playbooks are under control.
The first phase should target the assets where compromise would hurt most: servers, finance teams, leadership, remote users and devices with privileged access. That gives you a high-value view of risk without overwhelming the service desk or security team with every endpoint at once.
Keep the rollout disciplined:
A final misconception is that EDR deployment is mostly a licensing exercise. It is not. The real value appears when policies are tuned, escalation is defined and people know what to do the moment an endpoint starts behaving like an attacker foothold.